Signed receipts: verify what a check did on AI-written code, offline
A receipt is a signed statement of what a check did on an exact git tree. It replaces an agent's claim that tests pass with evidence anyone can verify with no account and no network.
What a receipt is
When 05's portable runner runs a check, it records the command, the result and the exact git tree it ran against, and signs that statement. The result can be a pass or a fail: a failing check is recorded too, and verifying that receipt says plainly that the check did not pass.
Because the receipt is bound to a tree, it cannot be reused for different code. Change a file and the tree no longer matches.
An open format, not a private one
- DSSE
- The Dead Simple Signing Envelope: a standard way to wrap a payload and its signature.
- in-toto statements
- The payload is an in-toto Statement v1, the format used for software supply-chain attestations such as SLSA provenance.
- Ed25519
- The signature algorithm. Keys are small and verification is fast.
Because the envelope is a standard, you are not locked into 05 to read it. An independent DSSE library, securesystemslib, verifies 05's receipts, and 05 verifies receipts made with it.
How it relates to SLSA and Sigstore
SLSA provenance is also an in-toto statement in a DSSE envelope, so tools that read in-toto attestations can read a 05 receipt's envelope. What is attested differs: SLSA provenance says how an artifact was built; a 05 receipt says what a check did on an exact git tree, and 05's other records hold the agent's declared plan, a person's approval and the seals on the agent's action log.
05 signs with keys you hold, and anyone with the public key verifies offline. It does not use Sigstore's keyless signing or a public transparency log, so nothing about your repository is published anywhere.
What it looks like
Real output from the current build.
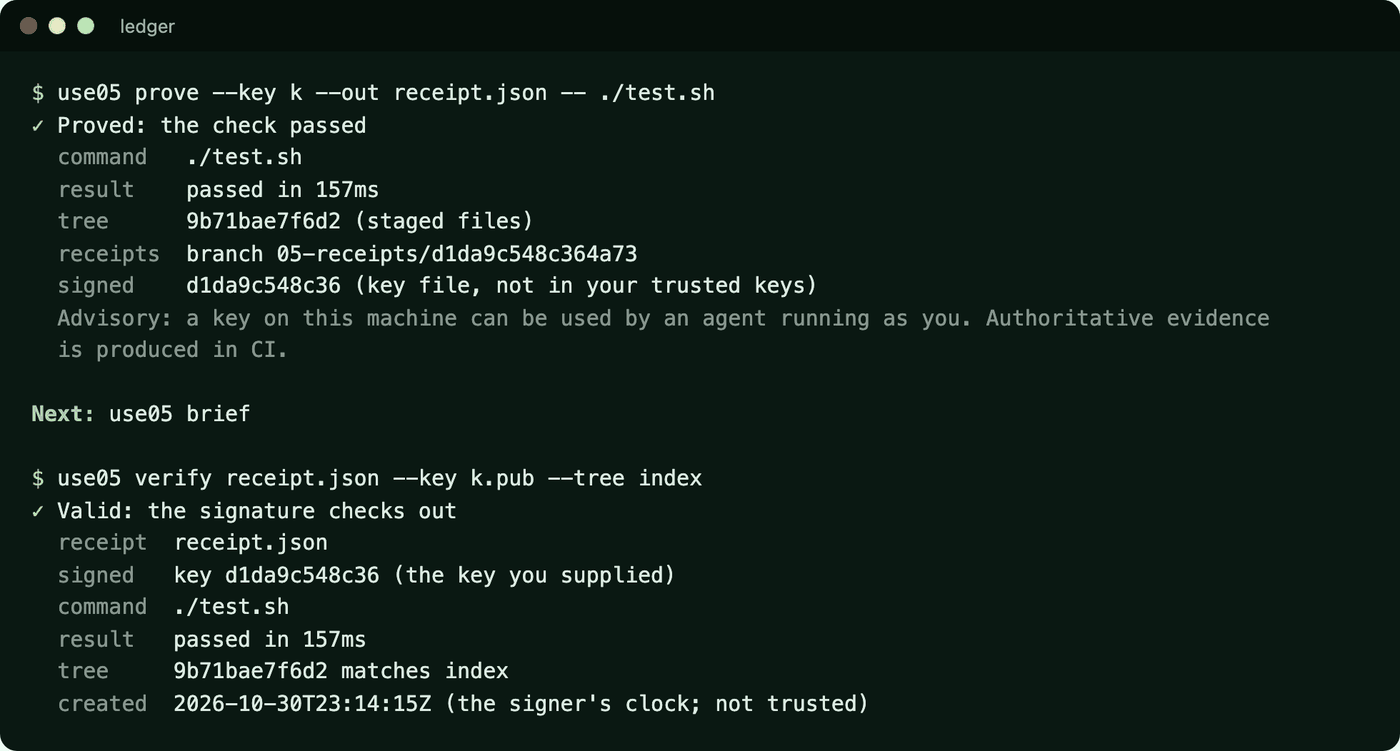
A passing check. Proved, then verified offline against the key you supply.
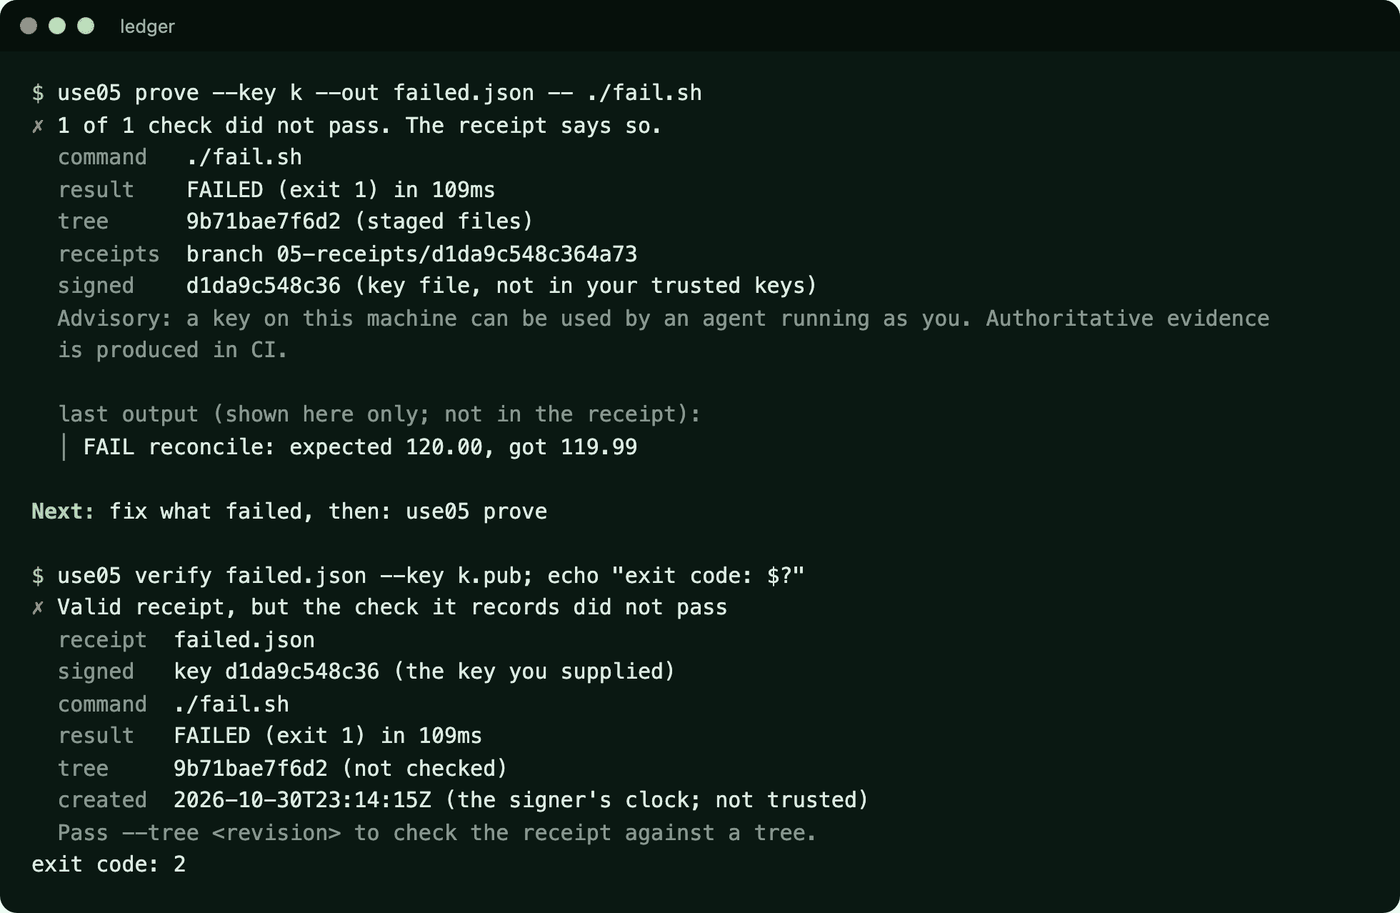
A failing check. A valid receipt that says the check did not pass, with exit code 2.
Measured on the current build
Measured, not promised.
- ≈ 10 ms to run
use05 verifyon a receipt, process start included. - 4.3 MiB for the whole
use05binary. - 5,717 single-byte edits to a real receipt. None changed what it says and still verified.
- Both ways: an independent DSSE library (securesystemslib) verifies 05's receipts, and 05 verifies its.
Measured on the current release build, in a dev container. Your machine will differ.
Strong signature, honest about where it was made
A signature proves who signed what, not that the signer was out of the agent's reach, so a receipt made on a developer's laptop is advisory until it is produced somewhere the agent cannot change, such as CI. The CLI prints this on every receipt it makes, and the enforcement page shows where each control runs.
Keep reading
Try 05 on your own repositories
The source, install steps and docs are on GitHub. Questions, or want to tell us which agent and Git host you use? Email us. No forms, no cookies.